Guardian — 24/7 monitoring
Endpoints and the network edge watched around the clock, with the authority to isolate a machine and stop an attack while it’s happening.
- Endpoint and network detection
- Containment in minutes
- Reports your insurer can read
Cybersecurity
Round-the-clock monitoring, phishing defense, testing, compliance and support, run as one program — watching your environment, testing it, training your people and proving it to auditors and insurers, so nothing falls between vendors.
One program
Most small businesses buy security one tool at a time: antivirus from one vendor, email filtering from another, a penetration test when an insurer asks. Each leaves gaps the next one doesn’t cover, and attackers walk straight through them.
Blue Ridge runs the whole lifecycle — watching your environment, pressure-testing it, training your people and proving it to auditors — so the pieces actually line up.
The platforms
Endpoints and the network edge watched around the clock, with the authority to isolate a machine and stop an attack while it’s happening.
One-click reporting, investigation, and removal of a malicious email from every inbox it reached — plus simulations and training.
Everything on your network discovered, what’s genuinely exploitable safely proven, and a short ranked list to fix.
Why Blue Ridge
Card terminals kept off guest Wi‑Fi, clinic systems separated from the front desk, production kept apart from the office.
When something is actively wrong, containment starts straight away, with on-site help across the Tri-Cities when it’s needed.
Whoever set up your security is who answers when it’s tested, so nobody starts from zero.
Controls mapped and evidence collected as the work is done, so an audit reviews work already finished.
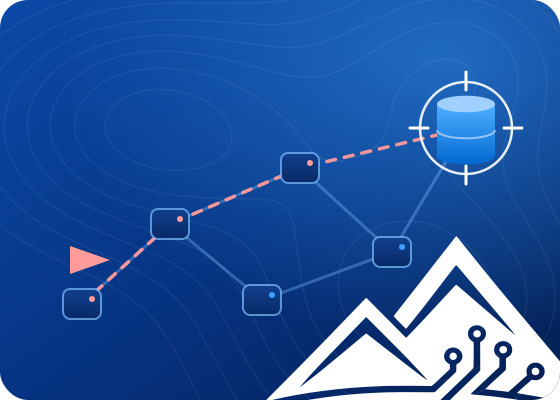
Red teaming
A penetration test finds vulnerabilities. A red team shows what happens when a skilled attacker chains them together — testing your people, processes and technology as one attack surface, against an agreed objective.
It’s uncomfortable by design, and only worth doing once the basics are in place. If they aren’t, you’ll hear that, and a penetration test first.
Dark web monitoring
Most businesses find out their passwords leaked when someone uses one. Credentials stolen in one breach get tried against email, banking and remote access everywhere else.
Blue Ridge watches the marketplaces, paste sites and stealer logs where they end up, verifies what turns up, and helps you close the exposure the same day — passwords reset, sessions revoked, multi-factor sign-in turned on.
A one-time scan of your domain shows what has already leaked, and is the usual starting point.
Compliance
Most compliance failures aren’t missing paperwork — they’re controls that exist on paper and not in practice. A policy says multi-factor sign-in is required; three accounts don’t have it.
Blue Ridge maps each requirement to a control that actually runs in your environment, writes the policies in plain language, and keeps the evidence current — gap analysis, a prioritised roadmap, implementation, then regular reviews.
No honest provider can guarantee you pass — the auditor decides. What Blue Ridge can do is make sure the controls are real and the evidence is ready.
Security support
Most businesses look for security help in the worst hour to do it — mid-incident, with systems down and nobody who knows the network.
A security support contract means the documentation, the access and the relationship already exist, so when something goes wrong the response starts from what’s known.
Getting started
Your networks, endpoints, policies and compliance gaps evaluated and documented.
A layered defense designed around your risk, with clear priorities and the price in writing.
Put in place, monitored and improved, with regular reviews to stay ahead of new threats.
From a client
Blue Ridge is a great company. Professional, knowledgeable, and efficient. I can’t recommend them enough for any and all cyber and physical security needs.
Questions
Something else? Call or text (423) 292-1922.
Usually with the basics that stop most attacks: multi-factor sign-in, tested backups, patched systems and staff who can spot a phishing email. An assessment shows which of those you already have.
No. Every business is different — the plan covers what yours needs and skips what it doesn’t.
Yes — it’s one of the most common reasons people call. The answers, and the evidence behind them, are part of the work.
A penetration test finds and validates weaknesses across your systems. A red team chains them together to show how far an attacker would actually get. Most businesses start with a penetration test.
No, but the accounts it opens can be secured: passwords reset, sessions revoked and multi-factor sign-in turned on.
Yes. Guardian, BlueHook and penetration testing all run alongside whoever manages your IT today.
Get in touch
Call or text, send an email, or leave a few details below. You’ll hear back from someone who knows the work, not a sales team.
